Dr Richard Horne warns the UK’s critical infrastructure could fail within two years due to escalating cyberattacks, threatening food and energy supplies.
Cyber chief warns of critical infrastructure collapse
Dr Richard Horne, CEO of the National Cyber Security Centre (NCSC), issued a stark warning on Tuesday 3 November 2026. He stated that Britain faces a genuine threat to its critical infrastructure within the next two years. This could lead to severe disruptions, including empty food shelves and widespread power outages.
Horne described an “unprecedented” surge in hacking activity. He cautioned that businesses could collapse if these cyberattacks are not urgently addressed. The NCSC chief emphasised the immediate need for action to bolster national resilience.
for decades, we have collectively got away with doing tech on the cheap.
Key warnings from the NCSC report
A new NCSC report highlights several critical concerns regarding the UK’s cyber security posture. It points to a significant increase in sophisticated threats.
- Dr Richard Horne predicts hostile actors will “highly likely” increase the scale and efficiency of their attacks by 2028.
- This escalation is attributed to artificial intelligence (AI) being used to exploit existing, long-tolerated vulnerabilities.
- The NCSC report specifically names Russia, China, and Iran as nations routinely employing AI to achieve their political objectives.
- Security minister Dan Jarvis acknowledged the growing sophistication of cyber threats.
- Jarvis stated the government is using AI to counter these threats, citing a new National Cyber Shield and an AI Cyber Security Centre of Excellence.
A decade of NCSC operations
The National Cyber Security Centre is marking its tenth year of operation in 2026. Its establishment aimed to centralise the UK’s cyber defence efforts against evolving digital threats. The NCSC has worked to protect critical national infrastructure and provide guidance to both public and private sectors.
Over this decade, the nature of cyber warfare has shifted dramatically. It has moved from isolated incidents to more coordinated, state-sponsored campaigns. The increasing sophistication of these attacks, now augmented by artificial intelligence, presents a new level of challenge.
Dr Horne’s comments reflect a long-standing issue within the technology sector. He noted that “for decades, we have collectively got away with doing tech on the cheap.” This historical underinvestment has created a landscape ripe for exploitation by advanced cyber tools, making current systems vulnerable.
Food and energy supplies at risk
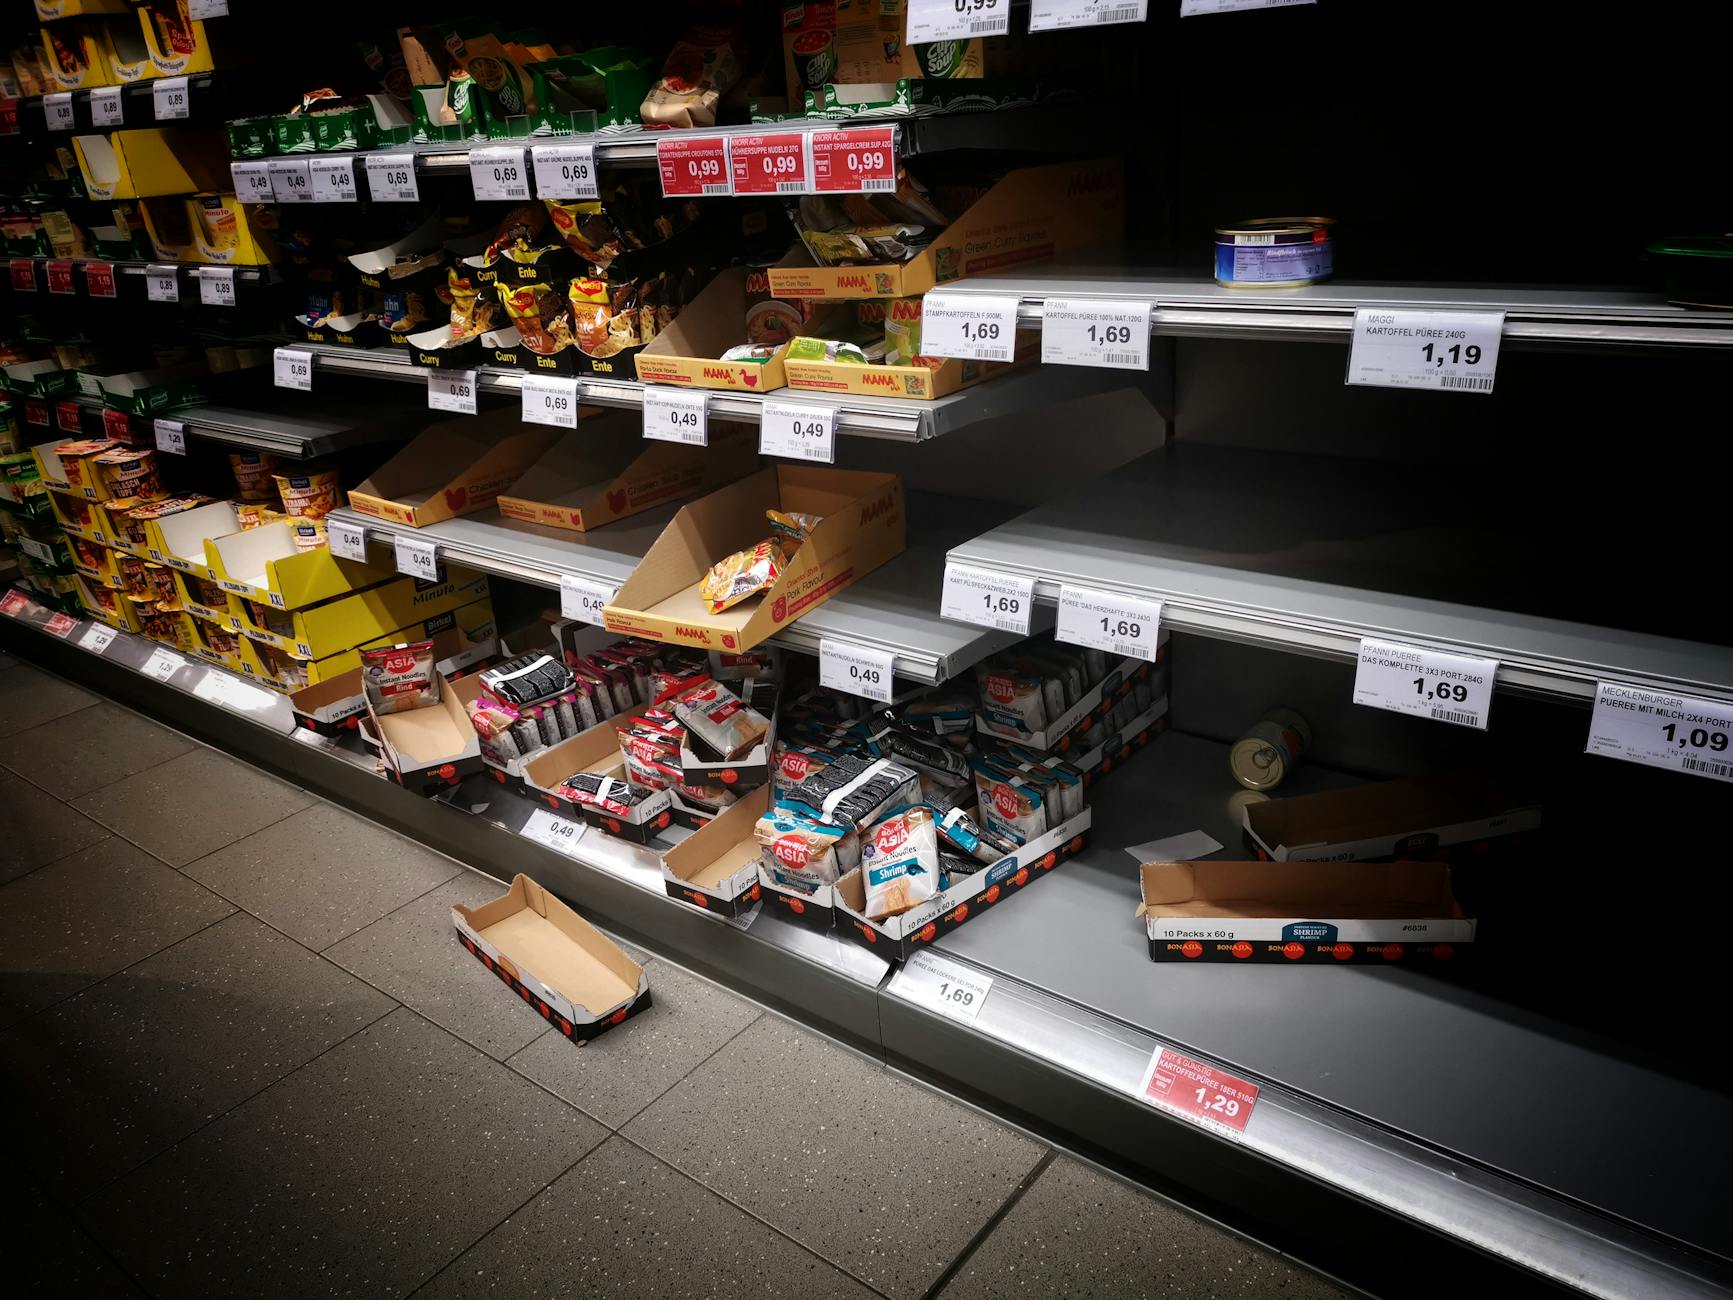
The immediate consequence of failing to address these cyber threats is a direct impact on daily life for every citizen. The NCSC chief explicitly warned of scenarios where “food isn’t on shelves, lights aren’t on, businesses have gone under.” Such disruptions would affect essential services and economic stability across the nation.
A collapse in critical infrastructure, including energy grids and supply chains, would have cascading effects. It would not only cause widespread inconvenience but also pose significant challenges to public safety and national security. The UK’s reliance on interconnected digital systems means a single point of failure could trigger widespread chaos.
The warning underscores the fundamental reliance of modern society on secure digital systems. Protecting these systems is no longer just a technical issue; it is a matter of national resilience and public welfare. The stakes are exceptionally high.
State actors escalate AI cyber warfare
The NCSC report identifies a clear pattern of state-sponsored cyber activity. Russia, China, and Iran are explicitly named as routinely using artificial intelligence to further their political goals. This represents a strategic shift from traditional espionage to more disruptive capabilities, targeting core national functions.
This trend mirrors broader geopolitical tensions where digital warfare has become a primary tool for influence and destabilisation. For instance, similar state-backed cyber operations have been observed globally, targeting elections, critical infrastructure, and intellectual property in other Western nations. The use of AI amplifies these threats.
AI allows hostile actors to discover and exploit vulnerabilities at an “unimaginable” scale. This capability transforms the threat landscape, making it easier and faster to launch complex attacks. The sheer efficiency offered by AI means that even long-standing, known weaknesses can now be weaponised with unprecedented speed.
Unclear investment specifics
The NCSC’s call for urgent investment raises a crucial question: how much funding is truly needed, and where exactly should it be directed? While the warning is clear, the specifics of the required financial commitment remain undefined.
- What is the estimated cost of upgrading the UK’s critical infrastructure to withstand these AI-driven threats?
- How will the new National Cyber Shield and AI Cyber Security Centre of Excellence specifically address the exploitation of “long-tolerated” vulnerabilities?
- What concrete timelines are in place for implementing these security enhancements across various sectors?
Investment must match evolving cyber threats
Dr Richard Horne’s warning is a critical alarm bell that the UK government and private sector must heed immediately. The idea that we have “got away with doing tech on the cheap” can no longer stand. Proactive, substantial investment in cyber security is not an optional expense; it is a fundamental requirement for national resilience.
Simply creating new centres or shields without addressing the underlying issue of neglected vulnerabilities will prove insufficient. The focus must shift from reactive defence to embedding security as a core principle. This applies to all new and existing infrastructure.
Prioritising secure design and continuous patching is essential. This will likely mean higher initial costs, but the alternative is far more expensive.